
3.6 Million Scam Pages: The Number Is Not the Most Important Part. The Best Scam Defence Starts Before You See the Scam
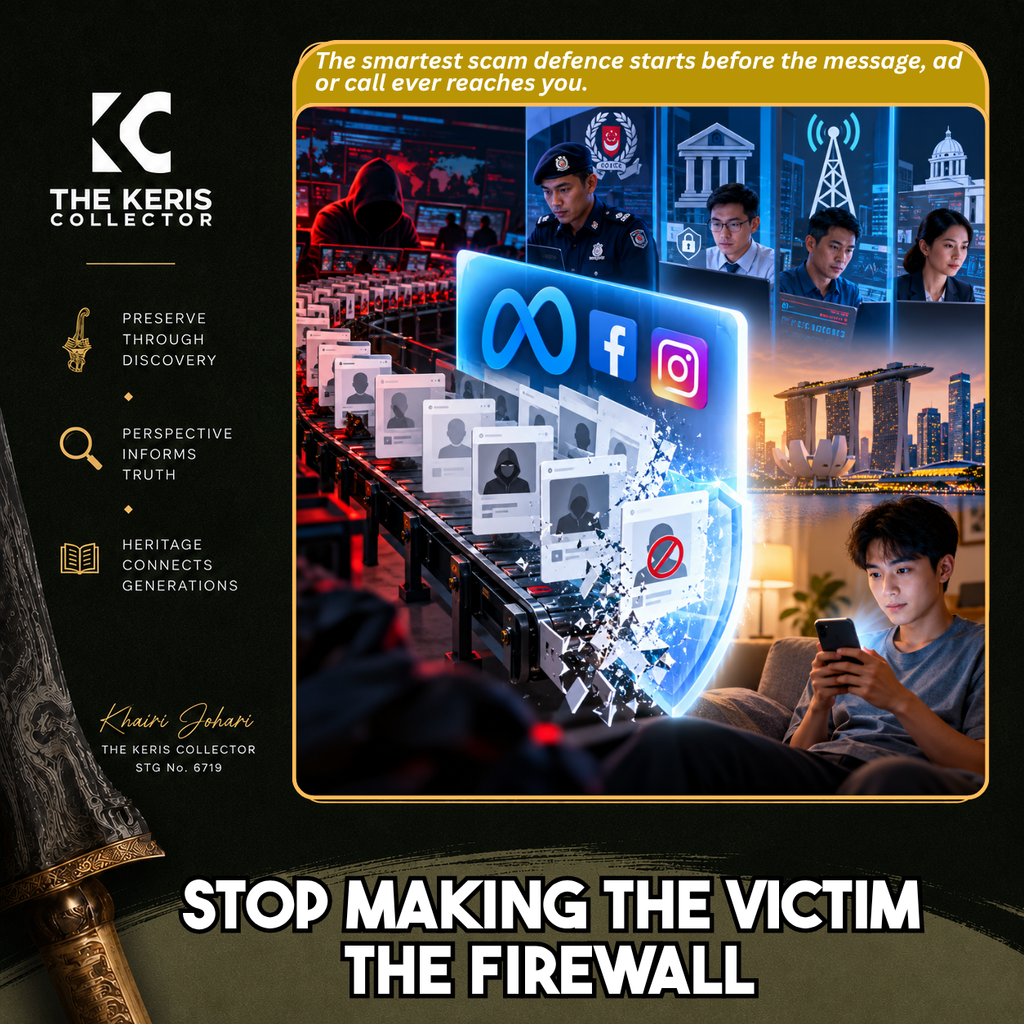
Meta says it acted against more than 3.6 million dormant “shell pages” identified through intelligence shared with the Singapore Police Force before those pages could be deployed in scam campaigns. The impressive number deserves caution, but the method points to something important: scam prevention works best when platforms, banks, telcos and law enforcement interrupt the machinery before an ordinary person has to recognise the deception.
When I first saw the headline about millions of scam-linked Facebook and Instagram pages being disrupted through cooperation between Meta and the Singapore Police Force, the number naturally caught my attention.
Nearly 3.8 million entities, pages and accounts sounds extraordinary.
But after looking at what actually happened, I think the more important story is not the size of the takedown. It is where in the scam process the intervention occurred.
Between January and June 2026, SPF referred more than 20,000 Meta accounts, pages and pieces of content after detecting signals associated with scam activity. Meta says it used that information to investigate wider networks rather than dealing only with the assets initially identified. That resulted in action against more than 113,000 scam- and fraud-linked entities and pages during the period, as well as more than 33,600 entities in a June operation focused on e-commerce scams.
Then came the unusual part.
In July, Meta says it acted against about 3.64 million “shell pages”. These were apparently empty or harmless-looking pages with no scam advertisements or other obvious violating content yet. According to Meta, they had been prepared as infrastructure that could later be activated for scam campaigns, and intelligence shared by SPF helped identify the pattern connecting them.
If that description is accurate, some of the infrastructure was disrupted before an advertisement appeared in somebody’s feed, before a scammer began talking to a potential victim and before anyone had to decide whether a message was genuine.
That is what interests me.
For years, much of the public conversation around scams has understandably focused on the person receiving the message. Slow down. Verify. Do not reveal your banking credentials. Do not transfer money just because somebody sounds authoritative. Use ScamShield. Check with someone you trust.
All of that remains necessary.
But it is also a very late line of defence.
By the time I am staring at a convincing fraudulent advertisement or talking to someone impersonating a bank officer, a considerable criminal system has already succeeded in reaching me. Accounts have been created. Advertising or messaging infrastructure has been prepared. Identities may have been stolen. Payment channels and money-mule accounts may already be waiting.
Then we ask the potential victim to make the correct decision.
That is a difficult way to defend millions of people against criminals who only need each victim to make one serious mistake.
The important shift is upstream
This latest operation did not invent preventive scam enforcement. Singapore has been moving in this direction for years.
The Online Criminal Harms Act already allows requirements to be imposed on designated online services to proactively disrupt scams. Facebook, Instagram, WhatsApp, Telegram and WeChat were among the services brought under the relevant code of practice in 2024, with measures aimed at reducing exposure to criminal activity rather than relying only on complaints after harm occurs.
Singapore has since gone further. In January 2026, the authorities issued Meta an Implementation Directive requiring additional measures against impersonation scams on Facebook, including enhanced facial-recognition measures and prioritised review of certain Singapore reports.
Telecommunications provide another example. IMDA says more than 260 million potential scam calls and 40 million SMS messages were blocked in 2025. It has also tightened SIM-registration controls and introduced measures that allow users to block incoming international calls and messages.
Banks are intervening further downstream, but still before money is lost. In a two-month operation this July and August, the Anti-Scam Centre worked with five banks using robotic process automation to identify potential victims. More than 2,700 customers received alerts, more than 400 ongoing scams were disrupted and SPF estimated that over S$46 million in potential losses was averted.
These interventions happen at different points in the chain.
The platform can see relationships between accounts that an ordinary Facebook user cannot. A telecommunications provider can identify suspicious communications patterns that the person receiving a call cannot see. A bank can detect transaction behaviour that looks very different when viewed across thousands of accounts. Police can combine intelligence from several parts of the system and, where jurisdiction permits, investigate the people behind it.
The individual citizen possesses none of those views.
That is why personal vigilance should be one layer of scam defence, not the whole architecture.
Big takedown numbers need one important qualification
There is a danger in becoming too excited by numbers such as 3.64 million.
Meta says those shell pages were identified as infrastructure associated with scam networks and acted against before they could be used. That is significant. It does not mean 3.64 million scams were prevented or 3.64 million Singaporeans were saved from becoming victims.
We do not know that.
Some pages may never have been activated. Criminals may rebuild infrastructure. Scam operations can migrate to other accounts, platforms and communications channels. Publicly available information does not tell us how many future victims those particular pages would have reached, what false-positive rate applied to the detection method, or how much criminal activity was permanently displaced rather than temporarily interrupted.
Those are important limits.
A takedown is an enforcement output.
The outcome we actually care about is fewer people being deceived, less money being lost, criminal networks becoming harder and more expensive to operate, and fraudulent infrastructure being detected faster than criminals can replace it.
Singapore’s wider scam figures offer some encouragement without proving that this particular Meta operation caused the improvement. MHA said reported scam cases fell 14.4 per cent to about 16,800 in the first half of 2026, while losses fell 17.9 per cent to roughly S$411 million compared with the same period a year earlier. The Government attributed that progress to a combination of public-private cooperation, enforcement, legislation and technology.
That is exactly how these results should be understood: as a system, rather than as one spectacular takedown solving the scam problem.
Platform responsibility and personal responsibility can coexist
None of this removes responsibility from the individual.
People still need to be careful with credentials, suspicious transfers, unfamiliar contacts and offers that appear too good to be true. There will always be scams that get through automated defences, and some criminals are exceptionally good at creating urgency, authority or emotional pressure.
Technology will never make judgement obsolete.
But I am increasingly uncomfortable with the idea that the main answer to sophisticated industrial-scale fraud should be asking every citizen to remain perfectly alert indefinitely.
The criminal has an asymmetric advantage. A scam syndicate can send thousands of messages, create thousands of accounts and test different approaches until something works. The potential victim only needs to be tired, distracted, frightened, lonely or overly trusting once.
That does not absolve reckless decisions. It does explain why a national anti-scam strategy cannot depend principally on perfect human vigilance.
Platforms therefore have responsibilities precisely because they can see and act on information ordinary users cannot. That does not mean demanding impossible perfection from them. Detecting malicious intent at scale is difficult. False positives matter. Legitimate businesses can be wrongly affected. Criminal networks adapt.
Proactive enforcement consequently needs safeguards, appeals and proportionate use of automated detection.
But the alternative cannot simply be allowing malicious infrastructure to remain in place until enough victims report it.
The purpose of prevention is to intervene earlier.
Fight the machinery, not only the message
What I find encouraging about the SPF-Meta cooperation is that it treats scams increasingly as an infrastructure problem.
Criminals need accounts, pages, communications channels, financial routes and identities. They need a way to find victims and a way to receive the money.
Every one of those dependencies creates an opportunity for disruption.
The strategic objective therefore does not have to be the impossible promise that Singapore will eliminate scams completely. It can be to make scams harder to launch, more expensive to scale, quicker to detect and less likely to reach the point where money changes hands.
The recent SPF-Meta operation illustrates one part of that model. Bank interventions illustrate another. Telecommunications blocking provides another.
And citizens remain part of it too.
The point is not to shift all responsibility away from individuals and onto institutions. It is to distribute responsibility according to who actually has the ability to act.
A citizen cannot inspect millions of Facebook pages and discover that apparently empty ones form part of a suspicious network. Meta can analyse that infrastructure.
Meta cannot freeze a suspicious bank transfer. A bank can intervene there.
A bank cannot investigate and arrest the people operating a syndicate. Police can pursue that where intelligence, law and jurisdiction allow.
Police cannot personally evaluate every message received by every person in Singapore. At some point, individual judgement still matters.
That complementarity is more important than any single takedown number.
Singapore should continue teaching people how to recognise scams. There will always be moments when someone’s judgement becomes the final barrier between a criminal and his savings.
But it should be the final barrier, not the barrier we rely on most heavily.
The best scam prevention happens before the victim has to make that decision at all.
CONCISE SOURCE / REFERENCE NOTE
The central figures come from SPF and Meta’s 23 September 2026 disclosures. SPF said enhanced information sharing contributed to Meta taking action against nearly 3.8 million scam-linked entities, pages and accounts during 2026. Meta said approximately 3.64 million of these were “shell pages” acted against in July before they could be used in scam campaigns. Neither source establishes that each page represented a separate scam or would have reached a Singapore victim.
Singapore’s broader preventive framework was checked against MHA’s Online Criminal Harms Act materials, current Meta implementation directives and IMDA’s anti-scam measures. One recent banking example was drawn from SPF’s September report on Anti-Scam Centre cooperation with DBS, UOB, OCBC, Standard Chartered and GXS, which disrupted more than 400 ongoing scams and estimated more than S$46 million in potential losses had been averted.
For national context, MHA reported about 16,800 scam cases and approximately S$411 million in losses in the first half of 2026, both lower than in the equivalent 2025 period. Those improvements cannot be attributed to the Meta operation alone.